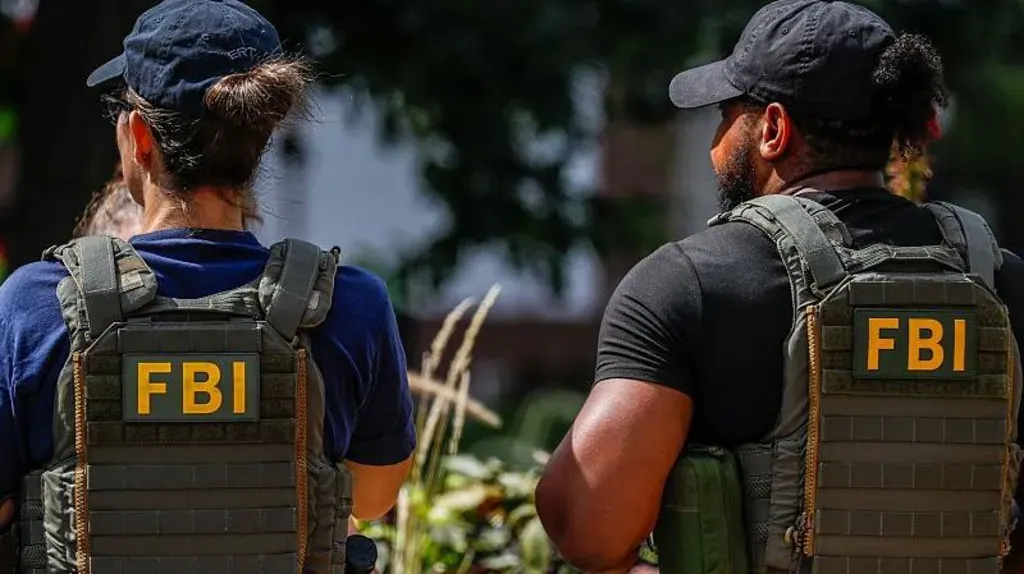
Cyber-criminals who hacked the FBI claim to have stolen extremely sensitive medical data for thousands of its special agents. The stolen data includes "fitness-for-work" medical examinations containing information such as blood and urine test results and doctors' notes mentioning various medical conditions. The records also include agents' full names and addresses, as well as references to medical concerns. Experts say the hack could leave agents vulnerable to scams, blackmail, and targeted attacks.
The hack, which the FBI is investigating, is believed to have been carried out by the cyber-criminal group ShinyHunters. The group claims it breached FBI systems and posted details of the attack on its darknet site. ShinyHunters shared samples of the alleged stolen data with reporters, along with an extortion demand. However, unlike typical ransomware attacks, the hackers are not demanding money; instead, they are seeking a retraction of an FBI advisory published in May.
The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles, and information about spouses. The records appear to relate to thousands of agents, including senior officials such as deputy directors. Professor Ciaran Martin, the former head of the UK's National Cyber Security Centre, described the hack as "serious as it gets when it comes to data breaches."
The breach may be more extensive than initially thought, with the hackers claiming to have underestimated the scale of the data theft. They now claim to hold sensitive information on around 60,000 current and former FBI staff, not just the 38,000 current employees initially reported. Experts warn that the stolen data could be used for highly convincing phishing, impersonation, identity fraud, blackmail, or even operations targeting law-enforcement personnel.
ShinyHunters claims it exploited a vulnerability in an Oracle cloud storage system used by the FBI, gaining access to multiple platforms, including FBIJobs, FBI BEAST, and FBI MedLink. The FBI has acknowledged the breach and said it was "aggressively investigating" how it happened. The agency is still trying to determine whether the hackers breached its systems directly or compromised a third-party provider.
The hackers, who communicate with reporters in English via the messaging service Telegram, say they will publish the full dataset in five days unless the FBI meets their demands. ShinyHunters is an international hacking collective that has been active since 2019 and has been linked to a number of high-profile cyber-attacks. The FBI has not responded to requests for comment.
The hack has raised concerns about the potential implications for national security and the safety of law enforcement personnel. Experts say the breach highlights the need for robust cybersecurity measures to protect sensitive information. The incident is under investigation, and the FBI is working closely with third-party providers to mitigate any and all risk.
Key points
- The hack could leave agents vulnerable to scams, blackmail, and targeted attacks.
- The breach may affect around 60,000 current and former FBI staff.
- The hackers are seeking a retraction of an FBI advisory published in May.