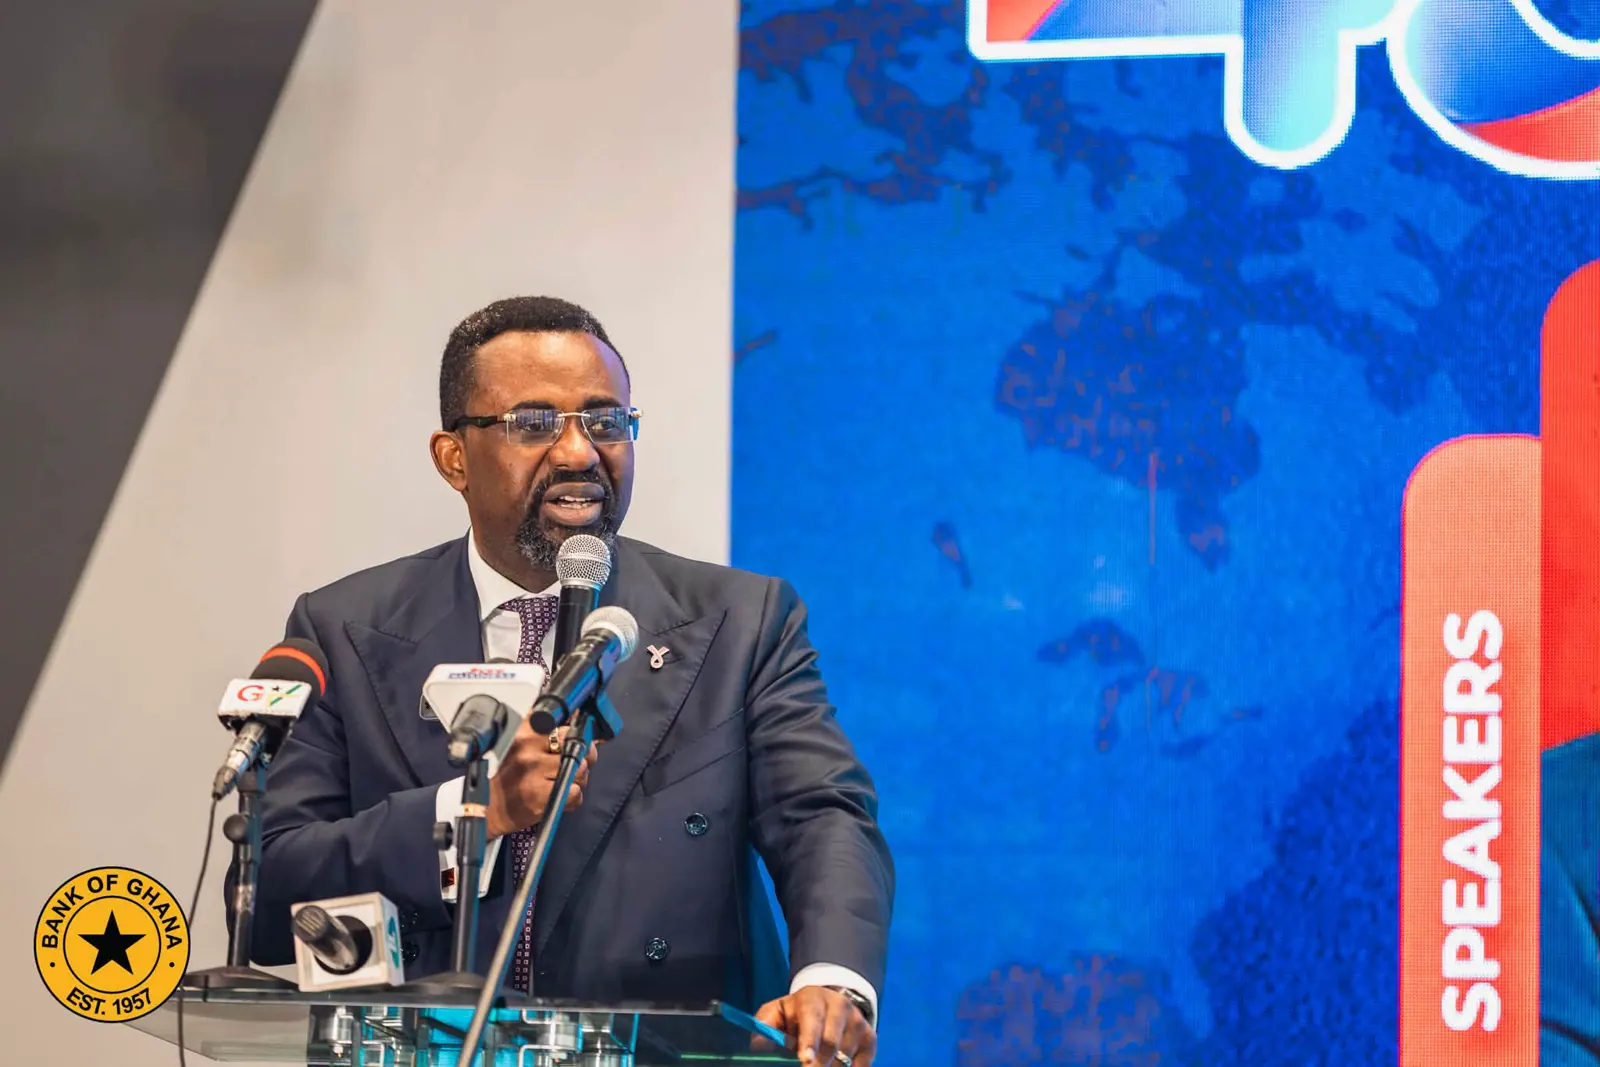
The Bank of Ghana (BoG) has announced plans to conduct thematic reviews of banks' compliance with its revised Cyber and Information Security Directive. This move is aimed at addressing growing concerns about digital fraud, cyber threats, and other risks associated with digital financial services. According to Dr. Johnson Pandit Asiama, Governor of the Bank of Ghana, the reviews will focus on areas such as cybersecurity, data protection, and operational resilience.
The announcement was made at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra. Dr. Asiama emphasized that digitalization has transformed financial services, improving efficiency, convenience, and financial inclusion. However, it has also created new channels for risks to emerge. He stressed that bank boards and senior management must treat cybersecurity and operational resilience as core business risks, rather than just technology issues.
The Bank of Ghana has been working closely with the Ghana Association of Banks and industry players to facilitate the implementation of the revised Cyber and Information Security Directive. The planned reviews are part of the Bank's broader supervisory efforts to strengthen the resilience of financial institutions in the face of evolving digital risks. Regulatory and supervisory frameworks must continue to evolve alongside technological developments and increasingly interconnected financial risks.
Dr. Asiama urged financial institutions to strengthen their risk-management frameworks and prepare for emerging threats. The changing financial environment requires institutions to be proactive in addressing potential risks. The Bank of Ghana's planned reviews will help ensure that banks are compliant with the revised directive and are taking adequate measures to mitigate cyber threats.
The meeting also marked the launch of the sixth edition of the GH Bankers' Voice magazine. The magazine is expected to provide insights into the banking sector and discuss key issues affecting the industry. The launch is seen as a positive development for the banking sector, as it provides a platform for stakeholders to engage with key issues.
The Bank of Ghana's move is seen as a response to the growing threat of cyber attacks in the financial sector. In recent years, there have been several reported cases of cyber attacks on financial institutions in Ghana. The planned reviews are expected to help strengthen the sector's defenses against such threats and ensure that banks are better equipped to manage risks.
The reviews will cover areas such as cybersecurity, data protection, cloud computing, third-party dependencies, and operational resilience. The Bank of Ghana's supervisory efforts are aimed at ensuring that financial institutions have adequate measures in place to mitigate potential risks. By doing so, the Bank aims to promote stability and confidence in the financial sector.
Key points
- The Bank of Ghana will undertake thematic reviews of banks' compliance with its revised Cyber and Information Security Directive.
- The reviews will focus on areas such as cybersecurity, data protection, and operational resilience.
- The move is aimed at addressing growing concerns about digital fraud, cyber threats, and other risks associated with digital financial services.