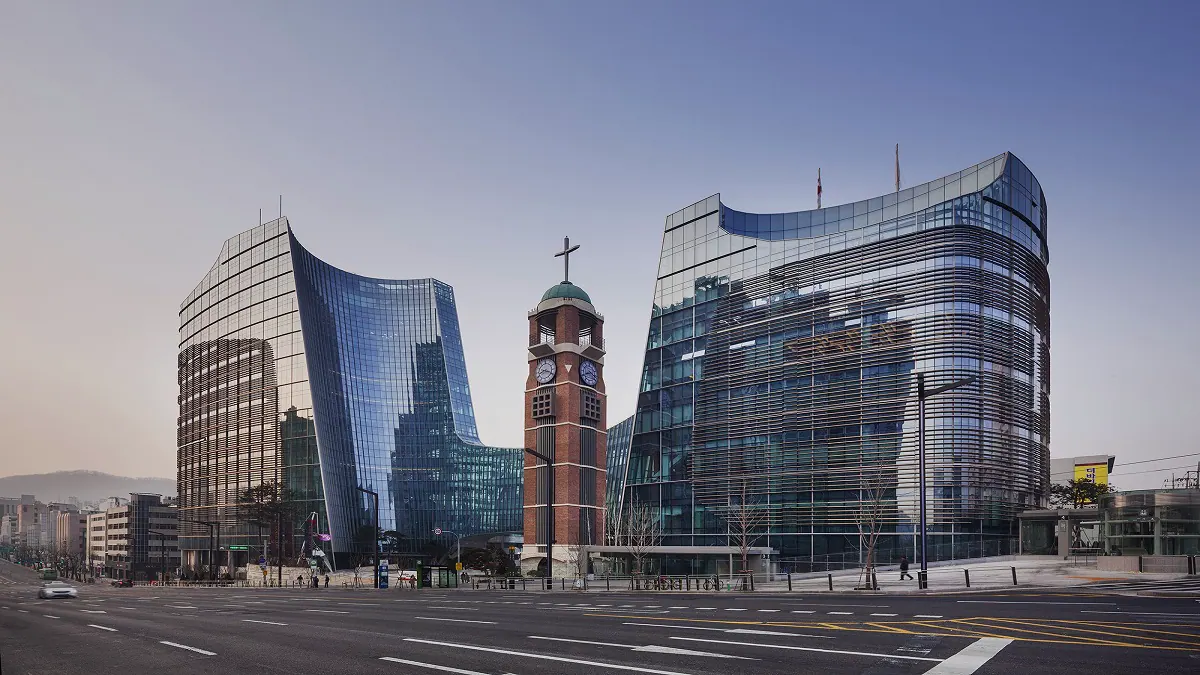
South Korea's Yoido Full Gospel Church has disclosed that personal information relating to 850,000 members may have leaked. The church's announcement followed an examination of files and access records after the Korea Internet & Security Agency alerted it to a suspected breach. Names, birth dates, and some contact-information records may have been compromised. The church is investigating the incident and taking measures to prevent further unauthorized access.
The affected material includes a file recording changes to members' information, with 2,629 records of changes to national identification numbers, 3,964 to telephone numbers, and 7,202 to addresses. These figures describe change records, not necessarily separate individuals. The church is notifying affected members, blocking external access, and changing server passwords. Senior Pastor Lee Young-hoon has apologized for the incident, stating that he feels a deep sense of responsibility for causing concern among members.
The church has qualified reports about leaked donation information, stating that historical donation documents examined contained voucher numbers, amounts, and transaction details without names or other personal identifiers. However, the church's review found personal information in one of seven suspected leaked documents. The church has removed malicious code and plans further security assessments and firewall upgrades to prevent similar incidents in the future.
Cybersecurity firm Oasis Security has discovered information linked to both Yoido Full Gospel Church and SaRang Church on an overseas server. The firm suggests that AI tools might have assisted the intrusions, but the role of AI remains unconfirmed. The investigation is ongoing, and the full scope of the suspected breaches is still being established.
The incident raises concerns about the information collected during routine administration by Nigerian churches and other organizations maintaining membership databases. Contact details and dates of birth can remain in a system long after their original purpose has passed, while change histories can preserve information that users believe they have replaced. Exposure could also make impersonation more convincing.
Yoido Full Gospel Church is continuing to assess the extent of the exposure and notify members. SaRang Church has established an emergency task force and reported a suspected incident to the authorities. The investigation is ongoing, and the church is working to prevent further unauthorized access.
The incident highlights the importance of robust cybersecurity measures for organizations maintaining sensitive information. Yoido Full Gospel Church's experience serves as a reminder of the potential consequences of a data breach and the need for vigilance in protecting personal information.
Key points
- Yoido Full Gospel Church reports possible data leak of 850,000 members' personal information
- The church is investigating the incident and taking measures to prevent further unauthorized access
- The incident raises concerns about the information collected during routine administration by organizations maintaining membership databases