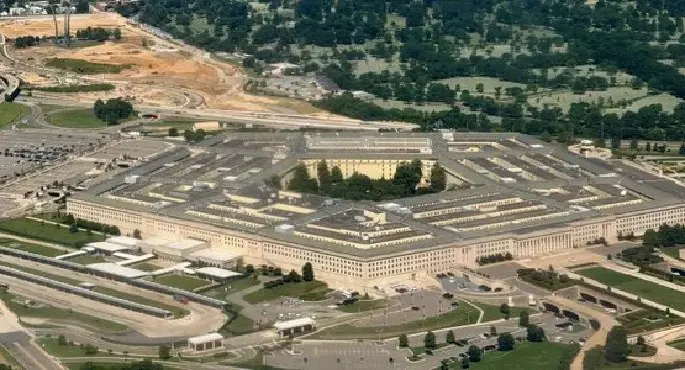
The US Department of Defense's personnel database, managed by the Defense Manpower Data Center (DMDC), was compromised in a cyberattack that began in October last year. The breach was not detected until July this year, nine months after it started. The attackers gained access to a computer server, compromising sensitive information, including social security numbers and personal data of current and former military personnel.
The breach is believed to have affected around 4 million individuals, according to the Military Times. The DMDC sent a notice to those affected, stating that unauthorized users accessed the server, but there is no evidence of misuse of the stolen data. However, the notice also warned that the breach may have exposed sensitive information, including job specialties, which could be used to identify individuals working in specific roles.
The stolen data was not encrypted, despite being a standard security practice to protect sensitive records. The breach has raised concerns about the vulnerability of military personnel data and the potential for foreign adversaries to use the information for malicious purposes. The US military has warned personnel about the risks of their personal data being targeted by adversaries.
The breach has significant implications, as it could allow adversaries to create detailed profiles of military personnel, including their job roles, and target them for recruitment or espionage. Justin Sherman, CEO of Global Cyber Strategies, said that combining the stolen data with commercial data sets could provide a comprehensive picture of an individual's online activities, financial information, and personal life.
The DMDC is a central repository for personnel data, supporting various government agencies, including the legislative branch, human services, national defense, and healthcare. The breach has highlighted the need for robust cybersecurity measures to protect sensitive information. The US military is taking steps to mitigate the risks and protect personnel data.
The incident has also raised concerns about the potential for phishing attacks and social engineering tactics to be used against military personnel. The US military has warned personnel to be vigilant and report any suspicious activity. The breach is being investigated, and measures are being taken to prevent similar incidents in the future.
The Pentagon data breach is the latest in a series of high-profile cyberattacks targeting government agencies and sensitive information. It highlights the need for robust cybersecurity measures to protect sensitive information and prevent similar breaches in the future. The incident is under investigation, and further details are being released as they become available.
Key points
- The breach exposed sensitive information of 4 million current and former military personnel.
- The stolen data was not encrypted, despite being a standard security practice.
- The breach has significant implications for military personnel, including the potential for targeted recruitment or espionage.