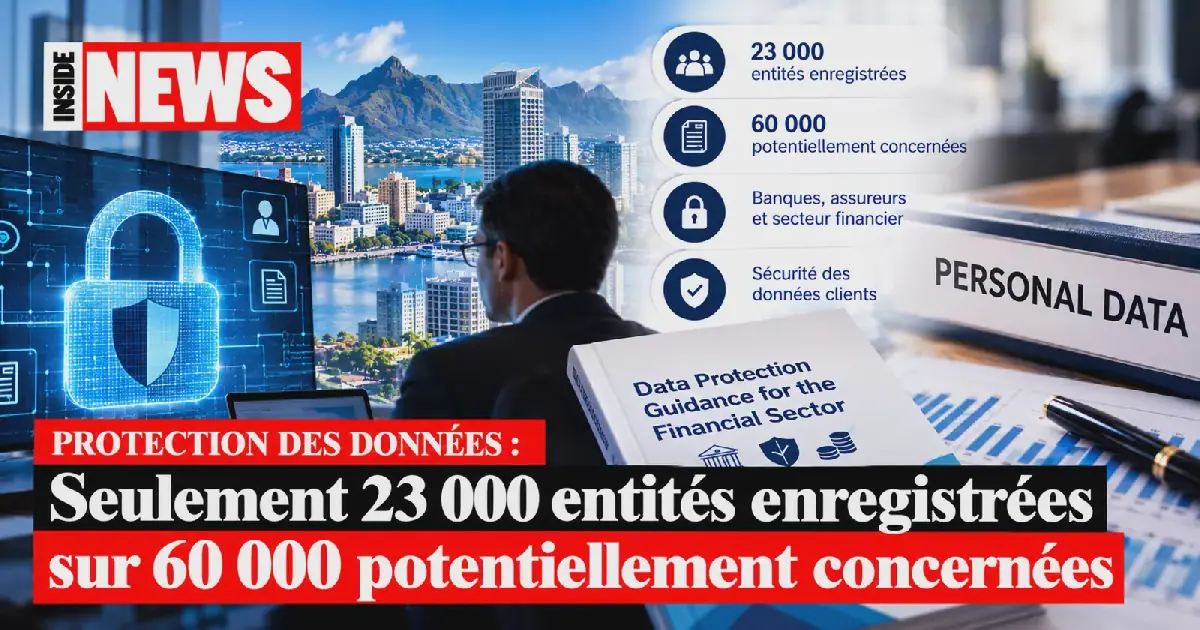
The Mauritian government has expressed concern over the low registration rate of entities required to comply with data protection regulations. According to recent statistics, only 23,000 entities have registered as data controllers or operators, while approximately 60,000 may be required to do so. This represents less than four registrations for every ten potentially concerned entities. The government has emphasized that this figure does not necessarily imply that the remaining 37,000 entities are non-compliant, as their status and activities require individual examination.
To address these concerns and strengthen data protection in the financial sector, the government has launched a new guide targeting banks, insurers, and other financial institutions. The guide provides recommendations on integrating data protection into management decisions, controlling service providers, and utilizing artificial intelligence. It also advises institutions to conduct Data Protection Impact Assessments for high-risk data processing, enhance incident preparedness, and improve cross-border data transfer controls.
The guide focuses on the protection of sensitive financial, transactional, and behavioral data. Financial institutions handling such data are expected to take proactive measures to safeguard client information. The government has stressed that mere administrative registration is insufficient and that audits, response exercises, and supplier controls will determine the effectiveness of data protection measures.
The Mauritian government is taking a multi-faceted approach to enhance data protection and cybersecurity. Plans are underway to establish a specialized cybersecurity agency and revise the Cybersecurity and Cybercrime Act 2021. Additionally, the government aims to strengthen training and certification programs for Data Protection Officers. These initiatives aim to bolster the country's data protection framework and ensure that institutions can prevent data breaches, detect intrusions, and inform affected individuals.
Client concerns center on the ability of institutions to protect their data and respond effectively in the event of a breach. The government has urged institutions to move beyond mere compliance and focus on implementing robust data protection measures. By doing so, institutions can ensure the security and integrity of client data.
The low registration rate has raised concerns about the level of compliance among entities in Mauritius. The government has encouraged entities to register and ensure they are taking necessary steps to protect client data. Failure to comply with data protection regulations can result in reputational damage and financial losses for institutions.
The government will continue to monitor the situation and take steps to enhance data protection in Mauritius. With the new guide and upcoming initiatives, the government aims to strengthen the country's data protection framework and ensure that institutions prioritize client data security.
Key points
- Only 23,000 entities have registered for data protection in Mauritius, despite an estimated 60,000 potentially being required to do so.
- The government has launched a new guide to strengthen data protection in the financial sector.
- Plans are underway to establish a specialized cybersecurity agency and revise the Cybersecurity and Cybercrime Act 2021.