The Kenyan government has successfully negotiated with Moldovan company B2bhint to delete sensitive information belonging to over 2 million businesses registered in the country. The data, which was stolen in February last year, included personal and business information of prominent investors such as President William Ruto, the Kenyatta family, and former Prime Minister Raila Odinga's family. The breach, which occurred through a bug in the State-owned Business Registration Service's IT system, exposed information such as company beneficial ownership and owners' identification details.
The data breach, which was discovered 18 months ago, revealed the business holdings of some of Kenya's most powerful figures. The leaked data included 812,863 phone numbers, 832,648 email addresses, 2,091,046 physical addresses, and the status of 2,093,194 firms. The information was sold on B2bhint's website for as much as Sh24 million for a package and as little as $0.015 for telephone numbers. The breach raised concerns over the security of government-held personal information and the potential exposure of business owners and company officials to identity theft, extortion, fraud, and other forms of abuse.
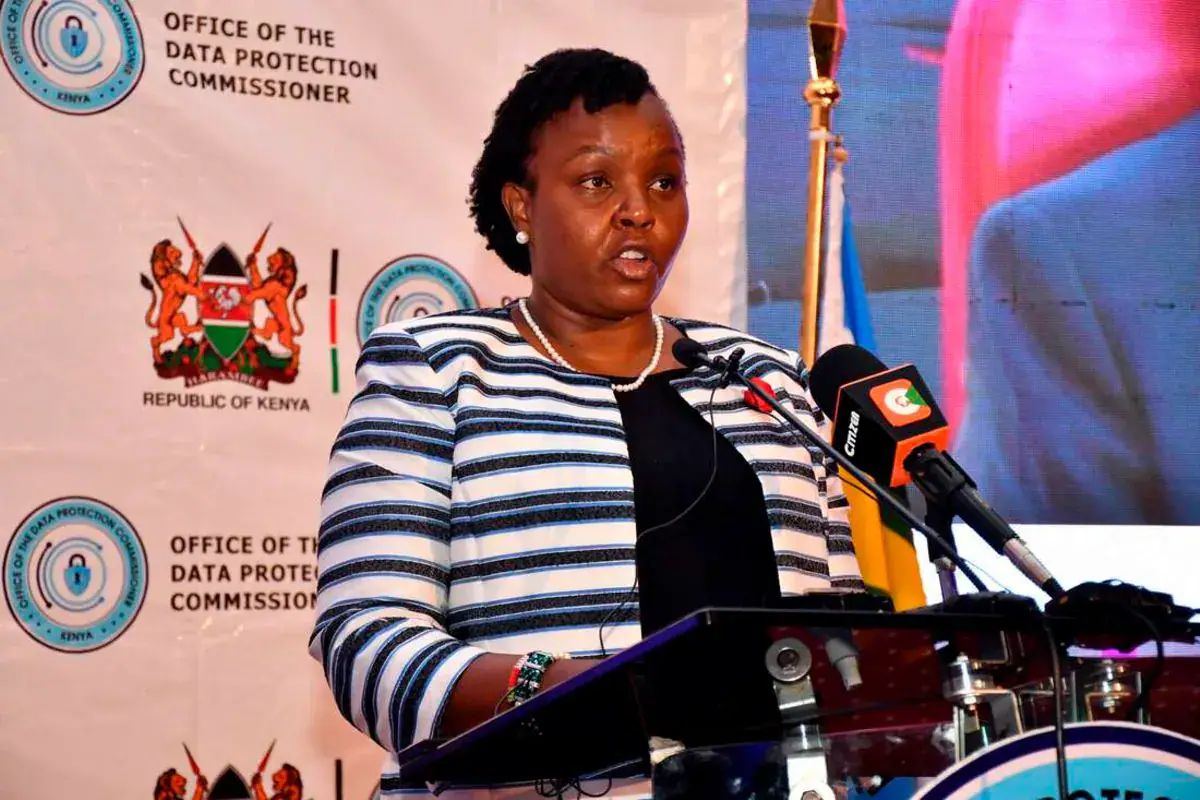
The Office of the Data Protection Commissioner, led by Immaculate Kassait, worked with the European Union Commission and the Moldovan data protection authority to track down B2bhint and compel it to delete the stolen data. Kassait revealed that the office faced jurisdictional challenges in investigating the breach due to the lack of mutual legal assistance agreements with foreign jurisdictions. The office issued an enforcement notice to the Business Registration Service, identifying weaknesses in its information systems and requiring the agency to strengthen its security measures.
B2bhint denied illegally hacking into the Business Registration Service's systems, instead blaming a weak cybersecurity standard for allowing it to access sensitive information. The company restricted access to the information on Kenyan companies after reports of the hack went mainstream and the Office of the Data Protection Commissioner initiated investigations into the breach. The Business Daily confirmed with B2bhint that it had permanently deleted the data after being requested by both Kenyan and Moldovan authorities.
The leaked data revealed the vast business interests of prominent Kenyan families, including the Kenyattas, the Odingas, and President Ruto's family. The Kenyatta family has interests in hospitality, dairy, real estate, and investments, while the Odinga family has interests in energy, logistics, real estate, and entertainment. President Ruto's family members, including his wife and two children, were listed as directors in several companies, including the Weston Hotel and Koilel Farm.
The breach occurred just weeks after the lapse of the December 1, 2024 deadline that required registered companies to disclose the names, phone numbers, and residential addresses of beneficial owners who hold more than 10 percent stakes through secret accounts to the Business Registration Service. The incident raised concerns over the security of government-held personal information and the potential exposure of business owners and company officials to identity theft, extortion, fraud, and other forms of abuse.
The Office of the Data Protection Commissioner investigated the breach and issued an enforcement notice to the Business Registration Service, requiring the agency to strengthen its security measures. The office has continued to follow up on the implementation of the recommendations. Under the Data Protection Act, 2019, data controllers, such as the Business Registration Service, are required to notify the Office of the Data Protection Commissioner of a breach.
Key points
- The Kenyan government brokered a deal with Moldovan firm B2bhint to delete stolen data of over 2 million businesses, including those linked to President William Ruto and the Kenyatta family.
- The data breach, which occurred in February last year, exposed sensitive information such as company beneficial ownership and owners' identification details.
- The Office of the Data Protection Commissioner worked with international authorities to track down B2bhint and compel it to delete the stolen data.
Reporting sources
- Moldovan firm erases leaked Odingas, Kenyattas’ dealings · Business Daily Africa