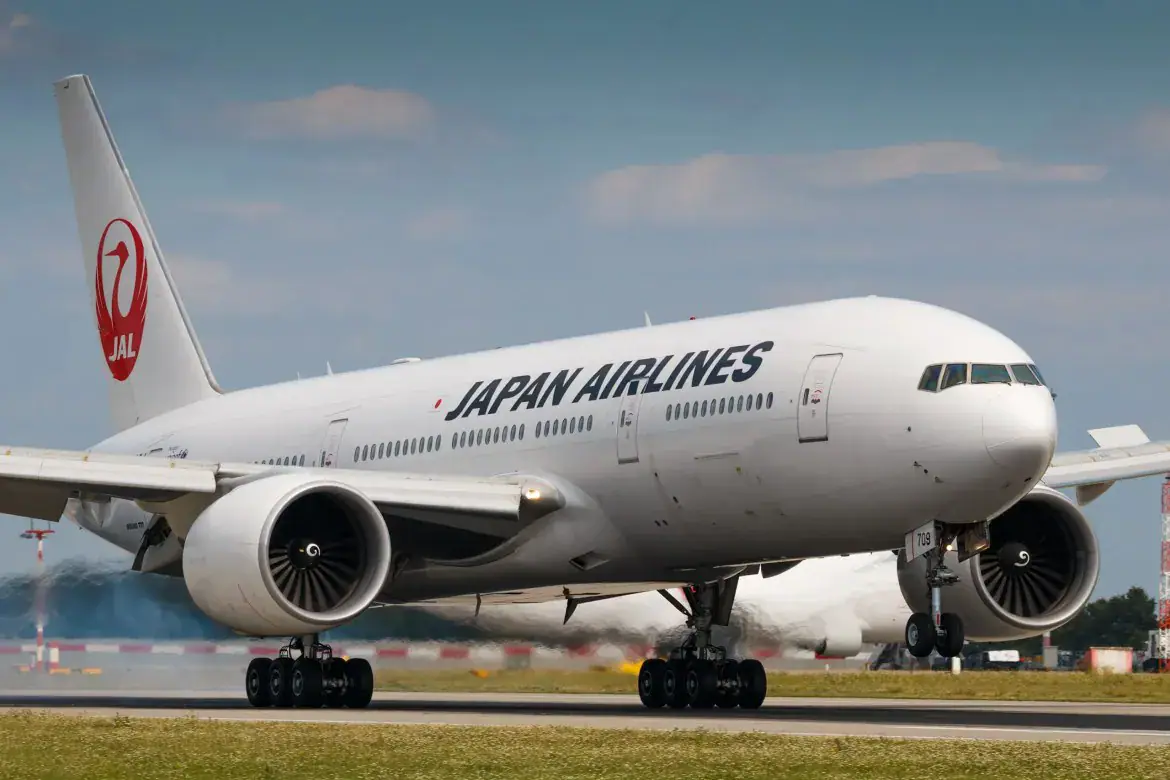
Two Japanese airlines, Japan Airlines (JAL) and Japan Transocean Air (JTA), have reported a security breach in their clients' reservation data. The breach occurred through their third-party passenger service system provider, Amadeus IT Group. According to JAL, approximately 92,000 customers may have had their reservation information accessed, including names, booking references, travel dates, flight sectors, and travel class.
The breach also exposed additional information for approximately 2,000 customers, including passport numbers, frequent flyer numbers, email addresses, phone numbers, and nationality. However, credit card numbers and passwords were not compromised. JAL was notified by Amadeus on October 23 and publicly disclosed the incident on October 28, 2026. The potentially affected reservation records span August 2023 to September 2026.
No impact on flight operations has been reported, and there is currently no evidence that the information has been misused. JAL will contact affected customers individually and has advised travelers to remain vigilant against phishing emails, fraudulent calls, and fake websites impersonating the airline. This incident highlights the risks associated with third-party IT providers and interconnected digital systems across the travel industry.
The disclosure comes amid a series of cyber incidents affecting Japanese businesses, emphasizing the importance of strong cybersecurity controls extending beyond airline-operated systems to the entire aviation technology supply chain. Protecting passenger data is a critical part of airline security. The incident serves as a reminder for airlines to prioritize data protection and be prepared for potential breaches.
In a separate development, Pakistan has reversed its decision to restrict Taiwanese airlines from using its airspace. The restriction was announced in support of Beijing's "One China" policy, affecting China Airlines and EVA Air. Both Taiwanese carriers were forced to reroute services between Asia and Europe. However, Pakistan's Civil Aviation Authority subsequently approved both airlines to use its airspace from October 28, 2026, to March 27, 2027.
The authorizations restored permission for Taiwanese airlines to overfly Pakistan, although the documents did not explain why the initial restriction was announced or why the position changed. Pakistani airspace is an important routing corridor for some Asia-Europe flights, and avoiding it can require longer routes, increasing flight times, fuel consumption, and operating costs.
The swift policy reversal by Pakistan highlights the importance of reliable and predictable overflight permissions for airlines. The decision-making process and diplomatic implications behind the initial restriction and subsequent reversal remain unclear. For airlines, having stable and consistent airspace permissions is essential to efficient international operations.
Key points
- Two Japanese airlines report data breach affecting 92,000 customers.
- Pakistan reverses airspace restrictions on Taiwanese airlines.
- Breach highlights importance of strong cybersecurity controls in aviation technology supply chain.