Emergency warning apps in Russia and Ukraine were hacked overnight, posting fraudulent alerts of imminent nuclear strikes, chemical hazards, and street warfare. The targeted applications serve as critical early-warning infrastructure, warning the public of missile, drone, and other threats. Officials in both countries confirmed the cyberattacks, but it remains unclear whether they were coordinated or linked. The breaches highlight broader vulnerabilities in state digital infrastructure amid ongoing regional conflict.
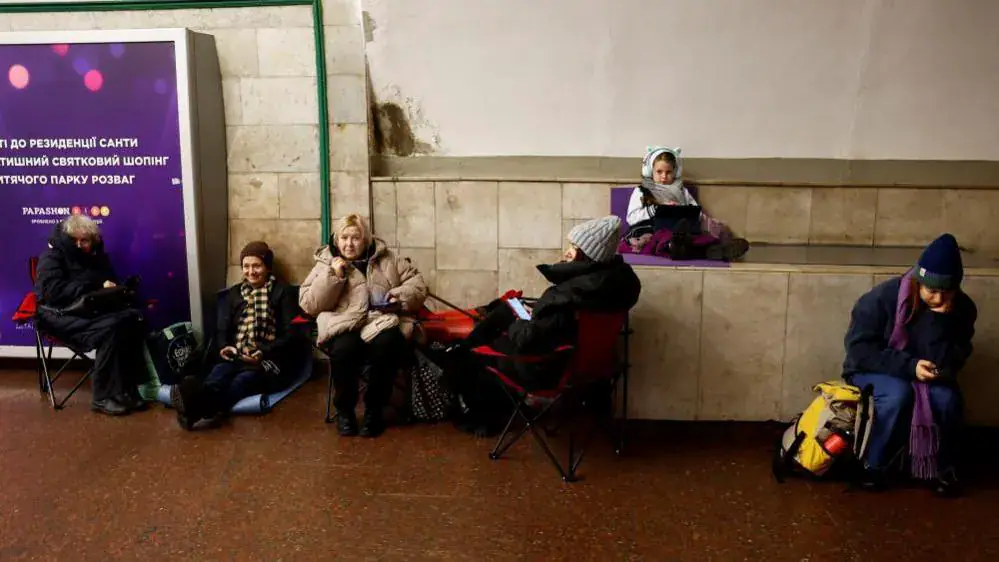
In Ukraine, hackers compromised the public air raid application, issuing unauthorized notifications claiming that Kyiv and several other regions were subject to nuclear and chemical alerts, as well as street combat threats. A fake message also claimed that Russia's hypersonic Oreshnik missile had been deployed. The intrusion targeted an application recently updated to show drone movements in real-time. Ukrainian officials quickly acted to reassure citizens, with the air force stating that there was no radiation threat and urging calm.
Stepan Tanasiychuk, who leads Ukraine's Air Raid Alert project, said technicians were restoring services, with new alert levels available on the map. The team is taking additional measures to secure the app and prevent similar situations in the future. Tanasiychuk acknowledged the unnecessary worry and inconvenience caused by the breach. Ukrainian defense authorities moved swiftly to contain the fallout and reassure citizens.
A separate cyberattack hit Russia's emergencies ministry app, resulting in the spread of false information to the public. A fake alert was sent to 33 Russian regions, claiming that nuclear warheads had been launched across all regions of Russia. Russian authorities moved to contain the operational fallout and reassure the domestic audience. The emergencies ministry said the app was currently operational and would be fully restored by the end of the day.
Russian authorities analyzed the incident and identified the vulnerability exploited by the attacker. The ministry downplayed the significance of the incident, stating that alerts are distributed through regional and municipal systems, such as sirens and loudspeakers, SMS messages, and media broadcasts. The breaches highlight the constant risk faced by state institutions in the region.
Kremlin spokesman Dmitry Peskov addressed the incidents during his daily news briefing, emphasizing the constant risk faced by state institutions. The high-profile breaches underscore the need for enhanced cybersecurity measures in the region. Peskov's comments suggest that the Kremlin is aware of the escalating cyber vulnerabilities and is taking steps to address them.
The incidents demonstrate the potential consequences of cyberattacks on critical infrastructure. The breaches caused unnecessary worry and inconvenience for citizens in both countries. Authorities in Russia and Ukraine are working to restore services and prevent similar situations in the future. The incidents highlight the need for continued cooperation and vigilance in the face of evolving cyber threats.
Key points
- Hackers breached emergency warning apps in Russia and Ukraine, posting fake alerts of nuclear strikes and chemical hazards.
- Ukrainian officials quickly acted to reassure citizens, with the air force stating that there was no radiation threat and urging calm.
- The breaches highlight broader vulnerabilities in state digital infrastructure amid ongoing regional conflict.