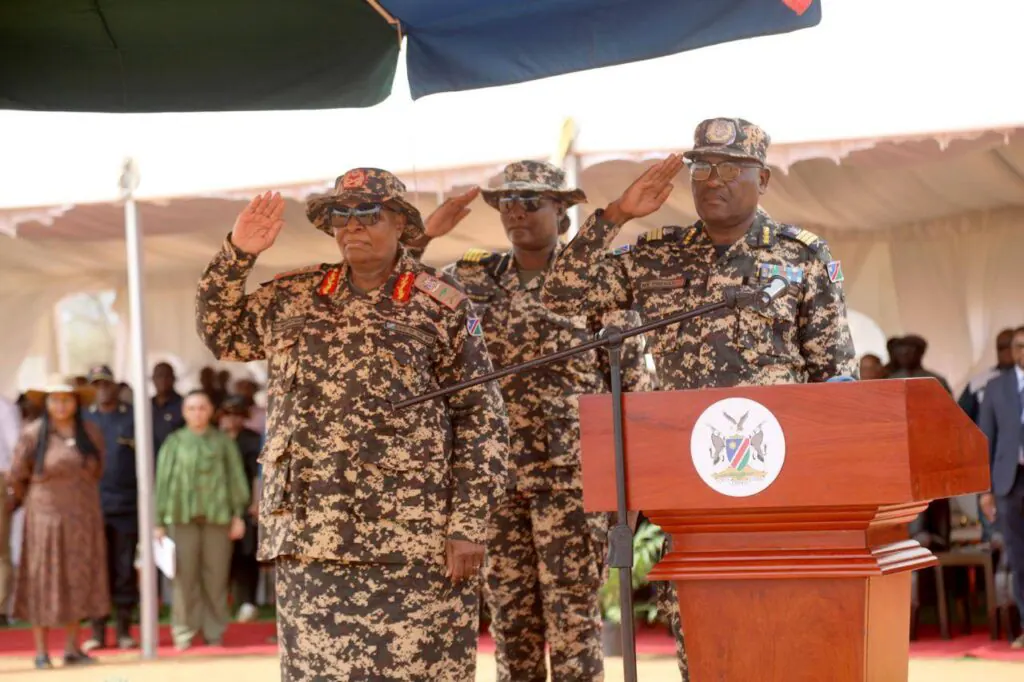
The Namibian Defence Force (NDF) has fallen victim to a ransomware attack by cybercrime group RansomHouse, which is threatening to leak confidential information. The hack, described as potentially "extremely dangerous" by an expert, occurred on Saturday. RansomHouse has listed the NDF as one of its victims and published an 'evidence pack' to demonstrate its access to the defence force's systems. The group also posted a message directed at NDF management, urging them to contact RansomHouse to prevent data leaks.
The attack comes as Namibia continues to work on laws aimed at dealing with cybercrime and protecting personal information. The drafting of the cybercrime bill was completed about six months ago, with the legislation expected to be submitted to parliament in March. Minister of information and communication technology Emma Theofelus stated in July that the cybercrime and data protection bills were being finalised. This incident highlights the need for robust cybersecurity measures and regulations in the country.
Minister of defence and veterans affairs Frans Kapofi expressed shock at the attack, stating he was unaware of its extent. He revealed that he had only been informed that the ministry was experiencing difficulties accessing some information, suspecting hacking. Kapofi claimed he had not been informed about RansomHouse or its threats to the NDF, saying, "This is the first time I'm hearing it, and I'm even shocked that there is such a thing."
The NDF has appeared on ransomware monitoring platforms tracking RansomHouse, including RansomLook and SOCRadar. SOCRadar classifies the threat as "data extortion" and recorded the NDF website in connection with a RansomHouse incident. However, SOCRadar's records raise questions about whether an earlier incident on 28 April is connected to the latest attack. The platform listed the victim as a 'Cybersecurity Vendor' in the technology sector with an 85% confidence rating.
This incident is not an isolated case, as Namibian organisations have been linked to other cybersecurity threats recently. In June, a global cybersecurity incident known as FortiBleed may have exposed administrator credentials and firewall configuration data at 13 Namibian institutions. The Namibia Cybersecurity Incident Response Team (Nam-CSIRT) reported over half a million cyber-vulnerabilities between April and June this year.
The Nam-CSIRT's second-quarter cybersecurity newsletter highlights the growing concern of cyber threats in Namibia. The team, housed at the Communications Regulatory Authority of Namibia (Cran), is working to address these vulnerabilities. The government is taking steps to strengthen cybersecurity, including the development of the cybercrime bill.
The ransomware attack on the NDF has significant implications for national security and cybersecurity. The incident underscores the need for increased vigilance and cooperation between government agencies, organisations, and cybersecurity experts to prevent and respond to cyber threats effectively.
Key points
- The attack highlights the need for robust cybersecurity measures and regulations in Namibia.
- The incident is not an isolated case, with Namibian organisations linked to other recent cybersecurity threats.
- The government is taking steps to strengthen cybersecurity, including the development of the cybercrime bill.