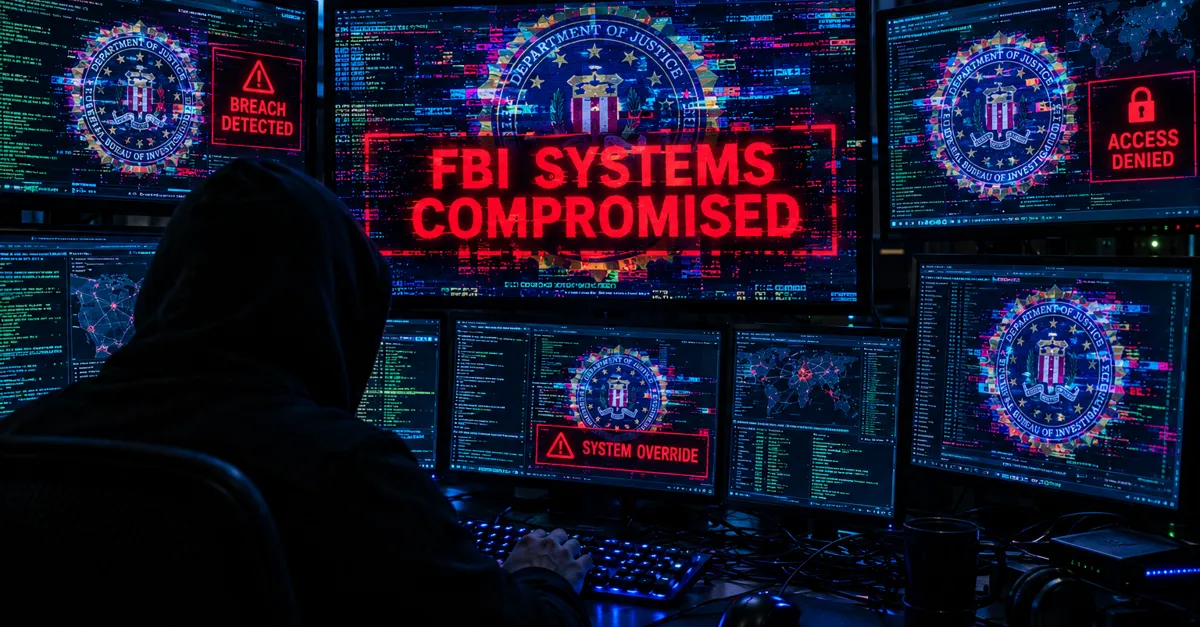
A recent breach in the Federal Bureau of Investigation's (FBI) employee database has resulted in the theft of sensitive personal data of thousands of current and former employees. The breach was carried out by a cybercrime group known as 'Shiny Hunters', who exploited a software vulnerability in the FBI's online employment portal. According to sources, the stolen data includes names, home addresses, social security numbers, and dates of birth.
The vulnerability exploited by the hackers was in the Oracle PeopleSoft system used by the FBI to manage its human resources. This vulnerability had been publicly disclosed in June, and the Cybersecurity and Infrastructure Security Agency (CISA) had warned that it posed a significant risk to federal agencies. Google's threat intelligence team had also detected a large-scale exploitation campaign by Shiny Hunters using the same vulnerability.
An analysis of the stolen data by The New York Times revealed that it included sensitive information such as phone numbers of spouses and emergency contacts, as well as details of employees' work assignments, including those related to counter-espionage and counter-narcotics operations. The data also included identification numbers used in the TSA PreCheck program, which could potentially be used to track the movements of undercover agents.
The FBI has acknowledged the breach and stated that it is working to investigate the incident and notify those affected. However, it is believed that many employees only learned of the breach through media reports, and were subsequently informed by the agency that their personal data may have been compromised. The FBI has urged employees to be vigilant and not respond to suspicious phone calls or emails.
The breach has raised concerns about the potential risks to the safety of FBI employees and their families. Experts have warned that the stolen data could be used to build detailed profiles of undercover agents, which could put them at risk of being compromised. The breach has also highlighted the vulnerability of the FBI's digital infrastructure and the need for improved cybersecurity measures.
This is not the first time that the FBI has been targeted by hackers. In 2015, a breach of the Office of Personnel Management resulted in the theft of sensitive data of over 20 million people. More recently, in 2024, Shiny Hunters hackers breached the systems of telecommunications company AT&T, stealing call and message records of some of its customers.
The FBI has stated that it is working to mitigate the risks associated with the breach and to prevent similar incidents in the future. The agency has also urged employees to take steps to protect themselves, including monitoring their credit reports and being cautious of suspicious phone calls or emails. The incident highlights the need for robust cybersecurity measures to protect sensitive data and prevent breaches.
Key points
- The breach has resulted in the theft of sensitive personal data of thousands of current and former FBI employees.
- The hackers exploited a software vulnerability in the FBI's online employment portal to gain access to the data.
- The breach has raised concerns about the potential risks to the safety of FBI employees and their families.